Account management#
Introduction#
LiveShield Manager supports multiple user accounts with different roles. A user’s Global Role defines default actions, Specific access limits resources for scoped accounts, and additional Permissions can grant rule creation or deletion.
Account management lives under Preferences in the sidebar footer. The page has two tabs:
Account settings: available to every logged-in user. Use it to change your own password and review your access and rule permissions.
Users: visible only to Administrators. Use it to create users, set roles, assign resources and additional permissions, and reset passwords.
The initial admin account is created during installation. See Base configuration for the first login, and installation, manager password for how the admin password is generated.
Note
There is no invitation or email flow for new users. There is also no delete-user action. To revoke functional access, set the user’s Global Role to NoAccess, clear all additional Permissions, and remove their Specific access assignments. Revoke any relevant API tokens separately.
Roles#
Each user has one Global Role. Roles are listed from most privileged to least. The actions below describe defaults before additional Permissions are granted:
Administrator: Full Manager access, including all resources and attacks, Users, Settings, Devices, Upstreams, Notifications, API tokens, and applying configuration.
SuperOperator: Can view all prefixes and attacks, use Reporting and the Executive dashboard, and create, edit, or delete Filtering resources and Manual Rules. Can manage Notifications. Cannot manage Users, Settings, Devices, Upstreams, or API tokens, or apply pending configuration.
Operator: Can view attacks and Reporting for assigned prefixes. Can view and edit assigned Filtering resources and Manual Rules within assigned prefixes. Cannot create or delete rules by default. No access to Settings, Devices, Upstreams, Notifications, or Users.
Viewer: Can view attacks, Reporting, assigned Filtering resources, and Manual Rules within assigned prefixes. Cannot edit, create, or delete rules by default.
NoAccess: Can log in and open Preferences to change password. Has no functional permissions by default. New users are created with this role and no additional permissions.
Important
Operator and Viewer only see resources assigned under Specific access. If no prefixes are assigned, their attack and Filtering Rules lists are empty. Other Filtering resource lists have their own assignments. Administrator and SuperOperator have unrestricted resource access; Specific access does not limit them.
Prefixes themselves (protected CIDRs / Filtering Rules) are configured under Filtering. See Detection and filtering.
For dashboard visibility by role, see Dashboard. Creating or editing a rule does not grant permission to apply configuration: an Administrator must click Apply in the sidebar to send pending changes to Analyser.
Account settings#
Navigate to Preferences in the sidebar. The Account settings tab opens by default.
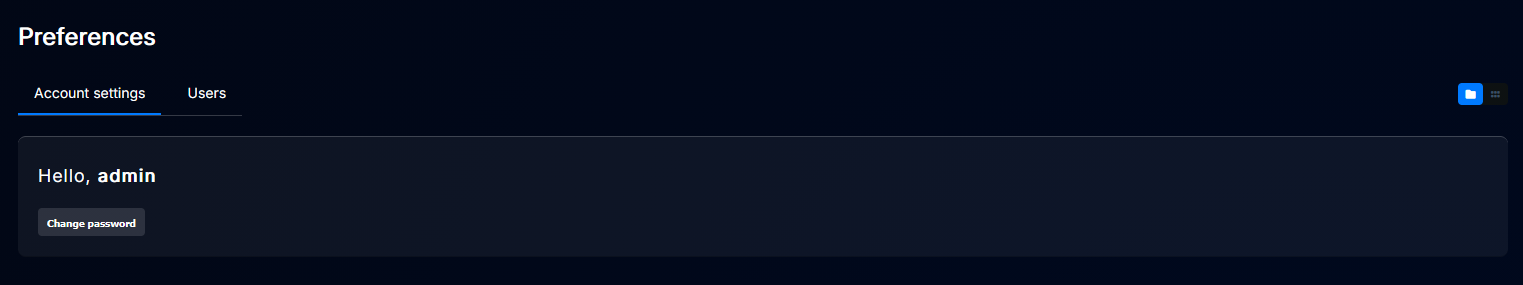
Click Change password. A dialog will appear where you can set a new password.

Settings explained:
Current password: Your existing password.
New password: Must be at least 8 characters and include at least one uppercase letter, one number, and one symbol. A strength meter is shown while you type.
Repeat new password: Must match New password.
Click Confirm to apply the change.
Hint
If you lost the admin password, you can reset it from the Manager installation wizard option [5] Reset admin password. See Installation.
Users#
Only Administrators can open the Users tab. Navigate to Preferences, then select Users.

The list shows Name, Global Role, and Actions for each user.
Adding a user#
Click the “+” button next to the Users title. A dialog will appear where you can create a new user.

Settings explained:
Username: Login name for the new account.
Click Create. The dialog closes and a popup shows the generated password once.

Warning
Copy the generated password immediately. It will not be shown again. If you lose it, use Reset password on the Users list.
The new user appears in the list with role NoAccess. Set a proper Global Role and assign resources after creation (see below).
Changing Global Role#
On the Users list, use the Global Role dropdown for the user. Options are Administrator, SuperOperator, Operator, Viewer, and NoAccess. The change is saved immediately.
Warning
You cannot change the role of the last remaining Administrator. The dropdown is disabled with the message that only one administrator is left.
Assigning resources#
Specific access controls which resources an Operator or Viewer can see. Assigning a resource does not change the user’s allowed actions: an Operator can edit assigned resources, while a Viewer is read-only unless separately granted a Create or Delete permission.
Click the edit (pen) action for the user. A dialog Edit user will appear.

Settings explained:
Username: You can rename the account if needed.
Specific access > Prefixes: Filtering Rules the user can access, shown as
{cidr} - {name}, for example192.0.2.0/24 - Customer A. These assignments also scope attacks, Reporting, and Manual Rules.Advanced Filtering Profiles: Profiles available to the user.
Prefix Templates: Filtering Rule Templates available to the user.
Blackholing Profiles: Blackholing profiles available to the user.
Event Pipelines: Pipelines available to the user.
Assign the supporting templates, profiles, and pipelines the user needs as well as the prefix. A prefix assignment alone does not grant access to every related resource.
Click Save when done.
Note
Specific access does not apply to Administrators or SuperOperators. Assigning a shared template or profile to an Operator lets them edit that resource, which can affect other prefixes using it. Choose these assignments accordingly.
To create the prefixes you want to assign, go to Filtering > Rules. See Detection and filtering.
Additional permissions#
In Edit user, the Permissions section has two groups:
Filtering rules: Create and Delete protected-prefix rules.
Manual rules: Create and Delete manual FlowSpec and blackholing rules.
Select the required actions and click Save. These permissions add to the role defaults; clearing a checkbox does not remove an action already granted by the role. They do not grant access to Settings, Users, Executive dashboard, or the Apply control, and do not remove resource scope restrictions.
For example, assign an Operator 192.0.2.0/24 and grant Filtering rules > Create to let them create a child prefix within that network. The newly created prefix is assigned to that user automatically. They cannot use this permission to create an unrelated prefix or change an existing prefix’s CIDR.
Grant Manual rules > Create to let a scoped user create rules whose Destination or Prefix lies within an assigned prefix. Delete allows removal of accessible rules. A Viewer with these additional permissions still cannot edit or toggle an existing rule. See Manual rules for details.
When upgrading to Manager 1.3.0, review existing Operator and Viewer assignments for all five resource categories. Users can review their assigned resources and effective rule permissions under Preferences > Account settings.
Resetting a user password#
On the Users list, click the reset password (asterisk) action. Confirm the reset in the popup, then a new password is shown once.

Warning
Password reset cannot be undone. Copy the new password immediately; it will not be shown again.